Detection Engineering versus Security Engineering
Detection engineering versus security engineering comes down to what each role is trying to change. Security engineers build and maintain controls that make systems harder to compromise. Detection engineers work with the signals those systems produce so suspicious activity can be identified, investigated, and acted on.
The two disciplines overlap, especially in cloud environments and smaller security teams. Both require knowledge of operating systems, networks, identity, cloud services, scripting, and security data. The difference becomes clearer when you look at the questions each person spends their day answering.
A security engineer may ask whether access controls, endpoint configurations, or network architecture reduce the chance of compromise. A detection engineer asks whether an attacker who bypasses those controls would leave evidence the security operations team can recognize.
Neither function operates well in isolation. Controls need visibility, and visibility needs controls that produce useful telemetry.
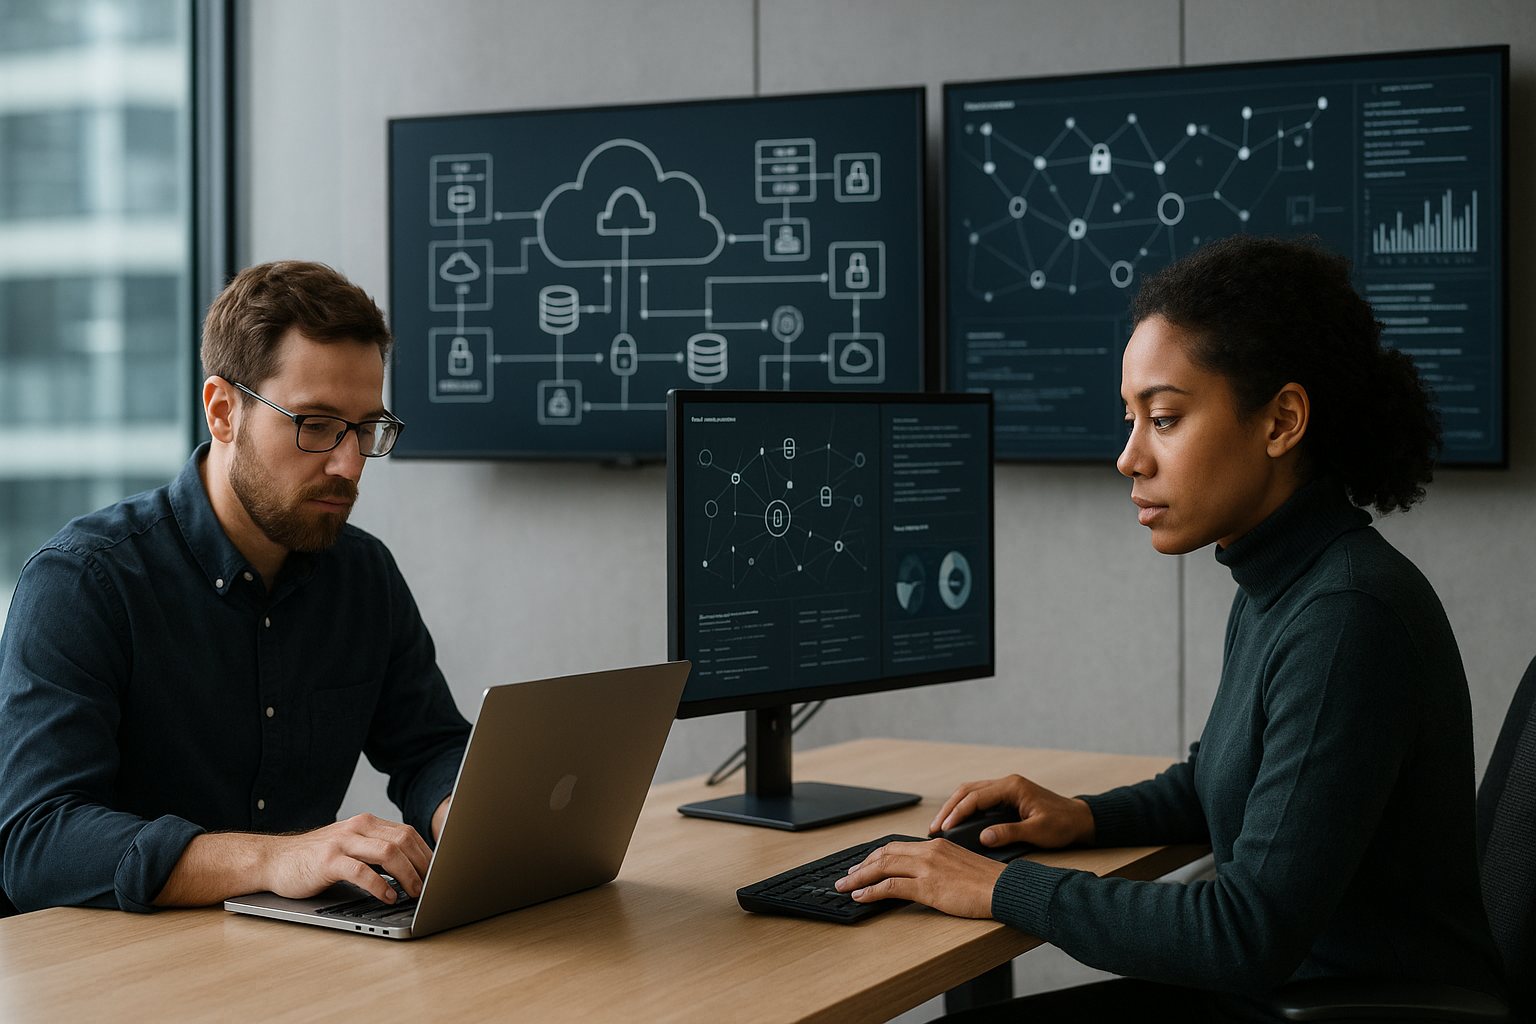
Two cybersecurity professionals collaborate in a modern cloud-security operations room, reviewing secure infrastructure settings, identity controls, suspicious activity alerts, and log visualizations.
Detection Engineers: Where Detection and Security Engineering Split
Security engineering has a broad technical remit. The work can include identity architecture, endpoint configuration, network security, vulnerability remediation, cloud controls, platform integrations, and secure system design.
The objective is to reduce exposure and make systems safer to operate.
Detection engineering has a narrower operational focus. It turns security telemetry into reliable detections that help analysts identify attacker behavior and decide whether an investigation is warranted.
A detection engineer may reproduce an attack technique, inspect the events it produces, build detection logic around those events, test the rule against normal activity, and tune it after analysts begin using it.
That leads to two different questions:
Security engineering: Can we prevent, contain, or reduce the opportunity for this activity?
Detection engineering: Can we see this activity, understand what happened, and give an analyst enough evidence to respond?
| Area | Detection engineering | Security engineering |
|---|---|---|
| Primary goal | Make suspicious activity visible and actionable | Make systems harder to compromise and safer to operate |
| Typical work | Build, test, tune, and maintain detections | Design, deploy, and maintain security controls |
| Main inputs | Logs, telemetry, attacker behavior, investigation outcomes | Architecture, configurations, access models, vulnerabilities |
| Common systems | SIEM, EDR, cloud logs, identity telemetry | Identity platforms, endpoints, cloud services, networks |
| Operational output | Alerts, investigation context, coverage information | Controls, secure configurations, integrations, remediation |
| Main feedback | False positives, missed behavior, investigations | Control failures, configuration drift, technical risk |
Job titles don't always follow these boundaries. A small security team may expect the same person to maintain the SIEM, configure security platforms, investigate alerts, and improve access controls. Larger organizations are more likely to separate the functions.
The work still follows the same distinction. One side changes the environment to reduce risk. The other makes hostile or suspicious behavior visible inside that environment.
How Threat Detection Turns Telemetry into Action
Detection engineering is usually immediately associated with writing a detection rule in a SIEM such as Elastic. Rule writing matters, but it's only one part of the job.
Security monitoring creates the raw material. Authentication events can show unusual sign-ins or privilege changes. Endpoint telemetry can record processes, command lines, file activity, and connections. Cloud audit logs show administrative actions. Network and application records add another view of what happened.
Detection engineering turns security telemetry into logic that answers a specific security question.
An impossible-travel alert is one example. Two sign-ins from distant locations may look suspicious, but the events alone don't prove an account is compromised. The analyst may need the identity, devices, authentication methods, timestamps, source addresses, and related sign-in activity before making that call.
The same applies to endpoint behavior. PowerShell execution alone is common. An unusual parent process launching an encoded command under an unexpected user account may deserve closer attention.
Detection quality depends on whether the alert carries enough context to separate useful signals from routine activity.
A workable detection process typically includes:
- Define a use case around attacker behavior or business risk.
- Confirm the required data is collected, parsed correctly, and retained long enough.
- Write detection logic using observable behavior.
- Test it against malicious and benign activity.
- Review alerts with analysts and record false positives or missed activity.
- Tune, replace, or retire the rule as systems and threats change.
This is a cyclical process. A rule that worked six months ago may become noisy after an infrastructure change. A new endpoint configuration may change the fields that reach the SIEM. An attacker technique may also change enough to bypass narrow logic.
Detection engineers have to keep testing what the platform can actually see.
That operational discipline matters for an MDR provider as much as an internal SOC. Alerts need to be understandable, explainable, and suited to the environment they protect. Creating large numbers of alerts without usable investigation context simply moves the problem to the analyst queue.
Detection Engineering vs Security Monitoring: What Both Roles Do in a Cloud Account
Cloud security shows how closely the two disciplines depend on each other.
Start with identity. Security engineering can separate human and workload identities, apply least-privilege permissions, require multi-factor authentication for privileged access, and review unused credentials.
Those controls reduce the opportunity for an attacker to gain or retain access.
Detection capabilities then need evidence showing when those controls are abused or bypassed. That means logging management activity, sign-ins, network flows, workload events, and relevant application activity in a location that investigators can access.
Once the telemetry exists, detection rules can look for activity such as:
- Unusual role or privilege changes.
- Access from unfamiliar locations or devices.
- Disabled logging or security services.
- Unexpected public storage exposure.
- Suspicious use of long-lived access credentials.
- Changes that fall outside approved configuration baselines.
An alert for a role change becomes far more useful when it contains the affected account, identity, asset, timestamp, source, and related events.
Configuration management adds another layer. Security engineers may establish approved baselines for encryption, backups, network settings, logging, and resource deployment. Monitoring can then identify unexpected drift from those baselines.
Some changes may be safe to remediate automatically. Others can affect production systems and require human review. The response should match the impact of the change rather than treating every deviation the same way.
The same principle applies after an alert fires. Teams need defined ownership for containment, evidence preservation, credential rotation, workload isolation, and communication before an actual breach forces them to make those decisions under pressure.
Penetration testing and controlled attack simulations can test both sides of the setup. They show whether controls resist the attack and whether monitoring records enough evidence when prevention fails.
Detection Engineer and Security Engineer Skills
Both paths need solid technical foundations. The difference is where that knowledge gets applied.
A security engineer often spends more time building and maintaining technical controls. That can mean configuring identity systems, hardening endpoints, designing cloud permissions, integrating platforms, automating deployment standards, or fixing weaknesses identified through vulnerability management.
A detection engineer works closer to attacker behavior and security operations. The role requires the ability to read logs, understand how an attack appears in telemetry, write queries, test assumptions, and judge whether an alert helps a SOC analyst.
Strong detection engineers typically need working knowledge of:
- Operating systems: enough depth to understand processes, authentication, services, files, and system behavior.
- Networks: protocols, connections, DNS, traffic patterns, and how attacks move between systems.
- Cloud services: identity, audit logging, workloads, permissions, and cloud-specific attack paths.
- Security DATA"9123" data-section-id="1v3ez3u" data-start="9025">Querying and scripting: enough to analyze events, automate work, and build repeatable tests.
- Adversary behavior: how attackers execute code, persist, escalate privileges, access credentials, and move through an environment.
- Investigation workflows: what an analyst needs to verify an alert and decide on a response.
Security engineers benefit from many of the same skills. Their work may place greater emphasis on architecture, automation, secure configuration, platform management, and implementing controls reliably across an environment.
Both roles also need to explain technical decisions clearly. It's not enough to say a configuration is safer or an alert looks suspicious. You should be able to explain what changed, what evidence supports the decision, what risk it addresses, and what the security team should do next.
Security and Detection Capabilities: How the Two Roles Strengthen Each Other
The strongest security programs connect prevention, visibility, investigation, and response.
Suppose a detection engineer repeatedly sees alerts caused by an overly permissive cloud role. Tuning the rule might reduce noise, but the underlying access model is still weak. That finding should reach the team responsible for identity controls.
A security engineer can then change the configuration.
The reverse happens too. A new endpoint policy may block one attack path but alter the telemetry reaching the SIEM. The control may work as designed while an existing detection quietly stops firing.
Detection engineers can identify that loss of visibility and work with the platform team to restore it.
Incident response creates another feedback loop. An investigation may reveal that logs existed but lacked the fields needed to reconstruct the attack. It may show that a detection fired too late, or that a control prevented part of the attack while another path remained open.
Those findings should become engineering work.
Security engineering can reduce the opportunity for the same attack. Detection engineering can improve visibility into the behavior that remains. The SOC can update its investigation process using what the incident exposed.
That is why treating these functions as completely separate security disciplines creates gaps. Controls should generate useful evidence. Reliable detections should expose weaknesses in controls. Analysts should feed investigation results back into both.
Detection Quality: Choosing the Security Path That Fits Your Work
Your preferred problems are a better guide than the job title.
Detection work may suit you if you enjoy investigating attacker behavior, working through messy data, writing detection logic, testing hypotheses, and figuring out why an alert fired or failed.
Security engineering may suit you if you prefer designing systems, configuring platforms, automating controls, securing cloud infrastructure, and solving implementation problems across an environment.
You don't need to treat the decision as permanent. The underlying technical knowledge transfers between the two. Experience with Windows internals can improve both endpoint hardening and endpoint detections. Cloud knowledge helps whether you're designing permissions or investigating suspicious role use. Scripting supports platform automation as well as telemetry analysis.
Halberd Security Academy focuses on the deeper technical knowledge behind security work rather than stopping at tool familiarity. Build the operating system, networking, security research, and detection skills that let you explain what the system is doing underneath the interface. Then test that knowledge against real behavior until you can show how your decisions affect prevention, visibility, and response.